Dynamic Application Security Testing (DAST)
Test running web applications, single-page applications and internal applications from the outside-in to identify exploitable security weaknesses.
Strengthen application and API security with Bright Security’s AI-powered testing platform. Discover vulnerabilities, validate real attack paths and bring actionable security feedback closer to developers and delivery workflows.
Meteonic helps organisations in India assess Bright Security for their application security, DevSecOps and continuous testing requirements.
Request a DemoTalk to an AppSec Expert
BRIGHT SECURITY AT A GLANCE
Bright Security provides an application security platform combining dynamic application and API security testing with AI-driven capabilities across software development workflows. Its capabilities include testing running applications, validating vulnerabilities, supporting remediation and integrating security testing into developer tools and CI/CD pipelines. Bright’s current platform also includes STAR capabilities for IDE, pull-request, AI-agent and non-HTTP application workflows.
MODERN APPLICATION SECURITY
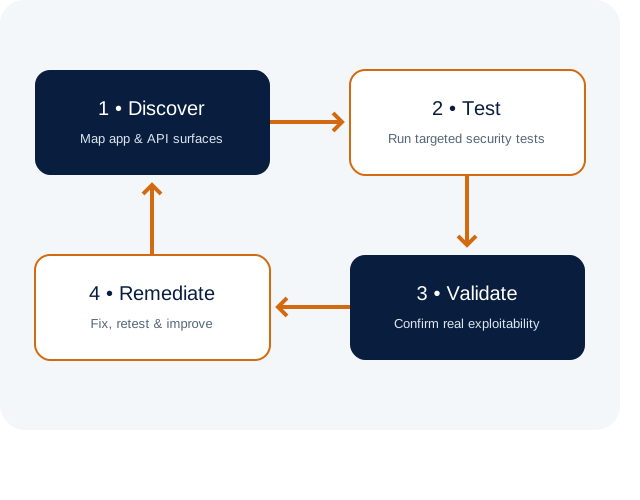
Traditional vulnerability lists can create friction when teams must manually determine which findings are reachable, exploitable and worth prioritising. Bright focuses on testing application behaviour and validating findings against real targets, helping security and engineering teams concentrate on actionable issues.
PLATFORM CAPABILITIES
Explore capabilities that help security and development teams test continuously and resolve verified vulnerabilities across the software lifecycle.
Test running web applications, single-page applications and internal applications from the outside-in to identify exploitable security weaknesses.
Assess REST, SOAP, GraphQL and other API surfaces for issues involving authentication, authorisation, input handling and sensitive data exposure.
Look beyond common vulnerability patterns to identify weaknesses in application workflows, business rules and multi-step transactions.
Evaluate AI-enabled application behaviour for risks such as prompt injection and other LLM-related weaknesses exposed through application interfaces.
Validate findings against real application behaviour to help teams reduce noise and prioritise vulnerabilities supported by evidence.
Connect security testing with developer workflows using supported IDE, CLI, API, repository, pipeline and ticketing integrations.
BRIGHT STAR
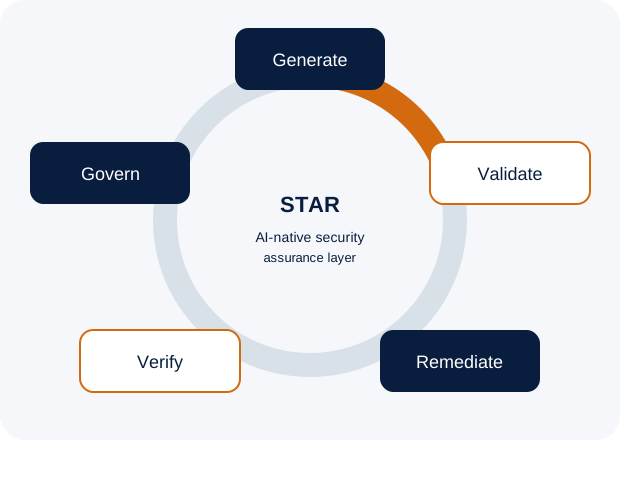
Bright’s current platform positions STAR as an AI-native security assurance layer for modern software development. It connects vulnerability discovery and exploitability validation with remediation context and verification, helping teams introduce security checks into AI-assisted engineering workflows.
Availability and supported integrations depend on the Bright subscription, deployment and product configuration.
WHERE IT FITS
Improve application coverage, validate vulnerabilities and provide evidence-led prioritisation across application portfolios.
Automate repeatable security checks in development and delivery pipelines while keeping feedback connected to engineering workflows.
Help teams address security issues earlier, improve remediation focus and support release velocity without treating security as a final-stage gate.
METEONIC • BRIGHT SECURITY IN INDIA
As a Bright Security reseller in India, Meteonic helps organisations understand the platform’s fit for their application landscape, security objectives and development processes.
Organisations looking for a DAST tool, API security testing platform, continuous application security testing or exploitability validation in DevSecOps workflows.
Relevant roles: CISO, CIO, CTO, AppSec leaders, Product Security, DevSecOps, Security Engineering and Application Development teams.
Speak with Meteonic about Bright Security for web application, API and AI application security testing.
Request a Bright DemoTalk to MeteonicANSWERS FOR APPSEC BUYERS
#305, 3rd Floor, Motiati Meadows, No.84-1-B,C.V.Raman Nagar, Bangalore-93 India
enquiry@meteonic.com
+91-6361414740